Buy technopa.eu ?
We are moving the project
technopa.eu .
Are you interested in purchasing the domain
technopa.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy technopa.eu ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **


Similar search terms for TPM
Top-Angebote
Products related to TPM:
-
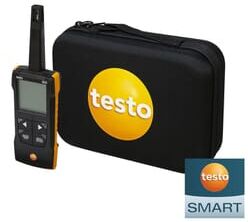
Testo 625 Digital Thermohygrometer – App ConnectedTesto 625 Digital Thermohygrometer with App Connection (0563 1625) The Testo 625 Digital Thermohygrometer is designed for quick, easy and precise measurement of air temperature and relative humidity. Well suited to assessing indoor air quality or maintaining optimal conditions in storage rooms, this compact device integrates with the Testo Smart App for enhanced functionality. The instrument automatically calculates dewpoint and wet bulb temperature, with time and point averages displayed instantly for quick assessment. Measurement data can be viewed as graphical curves within the app, saved, and managed alongside customer and site information, with reports emailed directly from the app. An audible alarm sounds if pre-set limit values are exceeded. Key Features & Benefits Precise M239,70 £*Shipping: 0,00 £Secure redirect to the provider
-
Inspire Essentials Smart App Connected Cat Water Fountain aGive your pet constant access to fresh, flowing water with a smart fountain designed for modern pet care. This automatic water fountain encourages healthy hydration by providing a continuous stream of filtered water that cats and dogs naturally...121,98 $*Shipping: 0,00 $Secure redirect to the provider

-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to TPM:
-
Asus TPM-SPI V2.0 Security TPM ModuleThe ASUS TPM SPI V2.0 Security Module is designed to enhance computer security by providing dedicated hardware based protection for compatible systems. It helps securely store encryption keys, digital certificates, passwords and other sensitive information. Using a 14-1 pin SPI interface, the module is designed for compatible ASUS motherboards and systems that support the TPM SPI standard. It provides a dedicated Trusted Platform Module solution for systems requiring hardware based security features. The module uses the Nuvoton NPCT750 security chip and complies with the Trusted Computing Group TPM 2.0 specification. This allows it to support security functions that help protect platform integrity and digital identities. Security certifications include Common Criteria EAL4+ and FIPS 140-2. The module also meets CE and RoHS compliance requirements, providing a certified solution for compatible computing platforms. The ASUS TPM SPI V2.0 is a compact internal security accessory designed for straightforward motherboard integration. Before installation, compatibility should be checked carefully because TPM SPI and TPM LPC modules use different pin definitions and are not interchangeable.15,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Testo 625 Digital Thermohygrometer – App ConnectedTesto 625 Digital Thermohygrometer with App Connection (0563 1625) The Testo 625 Digital Thermohygrometer is designed for quick, easy and precise measurement of air temperature and relative humidity. Well suited to assessing indoor air quality or maintaining optimal conditions in storage rooms, this compact device integrates with the Testo Smart App for enhanced functionality. The instrument automatically calculates dewpoint and wet bulb temperature, with time and point averages displayed instantly for quick assessment. Measurement data can be viewed as graphical curves within the app, saved, and managed alongside customer and site information, with reports emailed directly from the app. An audible alarm sounds if pre-set limit values are exceeded. Key Features & Benefits Precise M239,70 £*Shipping: 0,00 £Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
Similar search terms for TPM
-
Inspire Essentials Smart App Connected Cat Water Fountain aGive your pet constant access to fresh, flowing water with a smart fountain designed for modern pet care. This automatic water fountain encourages healthy hydration by providing a continuous stream of filtered water that cats and dogs naturally...121,98 $*Shipping: 0,00 $Secure redirect to the provider
-
Uplift Essentials Smart App Connected Pet Water Fountain (2.5L) 4pcs FiltersTake the guesswork out of your pets hydration with the Smart AppConnected Pet Water Fountain. This advanced hydration system integrates seamlessly with your smartphone, allowing you to monitor your pet's water intake in realtime from anywhere....56,97 $*Shipping: 0,00 $Secure redirect to the provider
-
BaByliss PRO Falco Advanced Professional High-Speed Digital Hair DryerAchieve the perfect finish with the Babyliss PRO Falco Advanced Professional High-Speed Digital Hair Dryer. FALCO's advanced high-speed digital motor delivers a strong, more precise air pressure and faster airflow. This hair dryer boasts precise heat and speed control with 3 speed settings and 4 temperature settings, helping you achieve perfect results on any hair type and texture. Ionic technology leaves hair with a smooth, shiny finish, free of frizz and fly-aways, making it much easier to detangle and style.185,00 £*Shipping: 0,00 £Secure redirect to the provider
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.